01 / 03
1. Resolve the intended name
- On the client run getent ahosts YOUR_HOSTNAME, replacing the placeholder with the authorized DNS name.
- Compare the returned addresses with the service owner's inventory and note whether IPv4 or IPv6 is in use.
- On the server run ip -br address to inspect assigned addresses.
You should seeA DNS answer identifies an address, not a working service. If it is absent or unexpected, resolve DNS with its owner before changing firewall rules.
02 / 03
2. Inspect the server listener
- On the server run sudo ss -lntp and locate the expected TCP port and process.
- Check whether the listener binds the intended interface or only loopback.
- From an approved client, use the application or a permitted TCP connection check to that host and port.
- Before you use it
- Run on the authorized server; compare its ports to the service inventory.
ss -lntuCaptured demo response · 2026-11-04T08:44:38.886099Z. Any filtering, hidden values or test-only data are identified in the capture label. Select Replay transcript to read the recorded output.
- Success looks like
- The lab returned listening sockets; deployment-specific addresses are masked in the image. A listener does not prove external reachability.
- Stop if
- If the expected listener is absent, inspect the service before changing network policy.
Observed listening sockets
Open to enlarge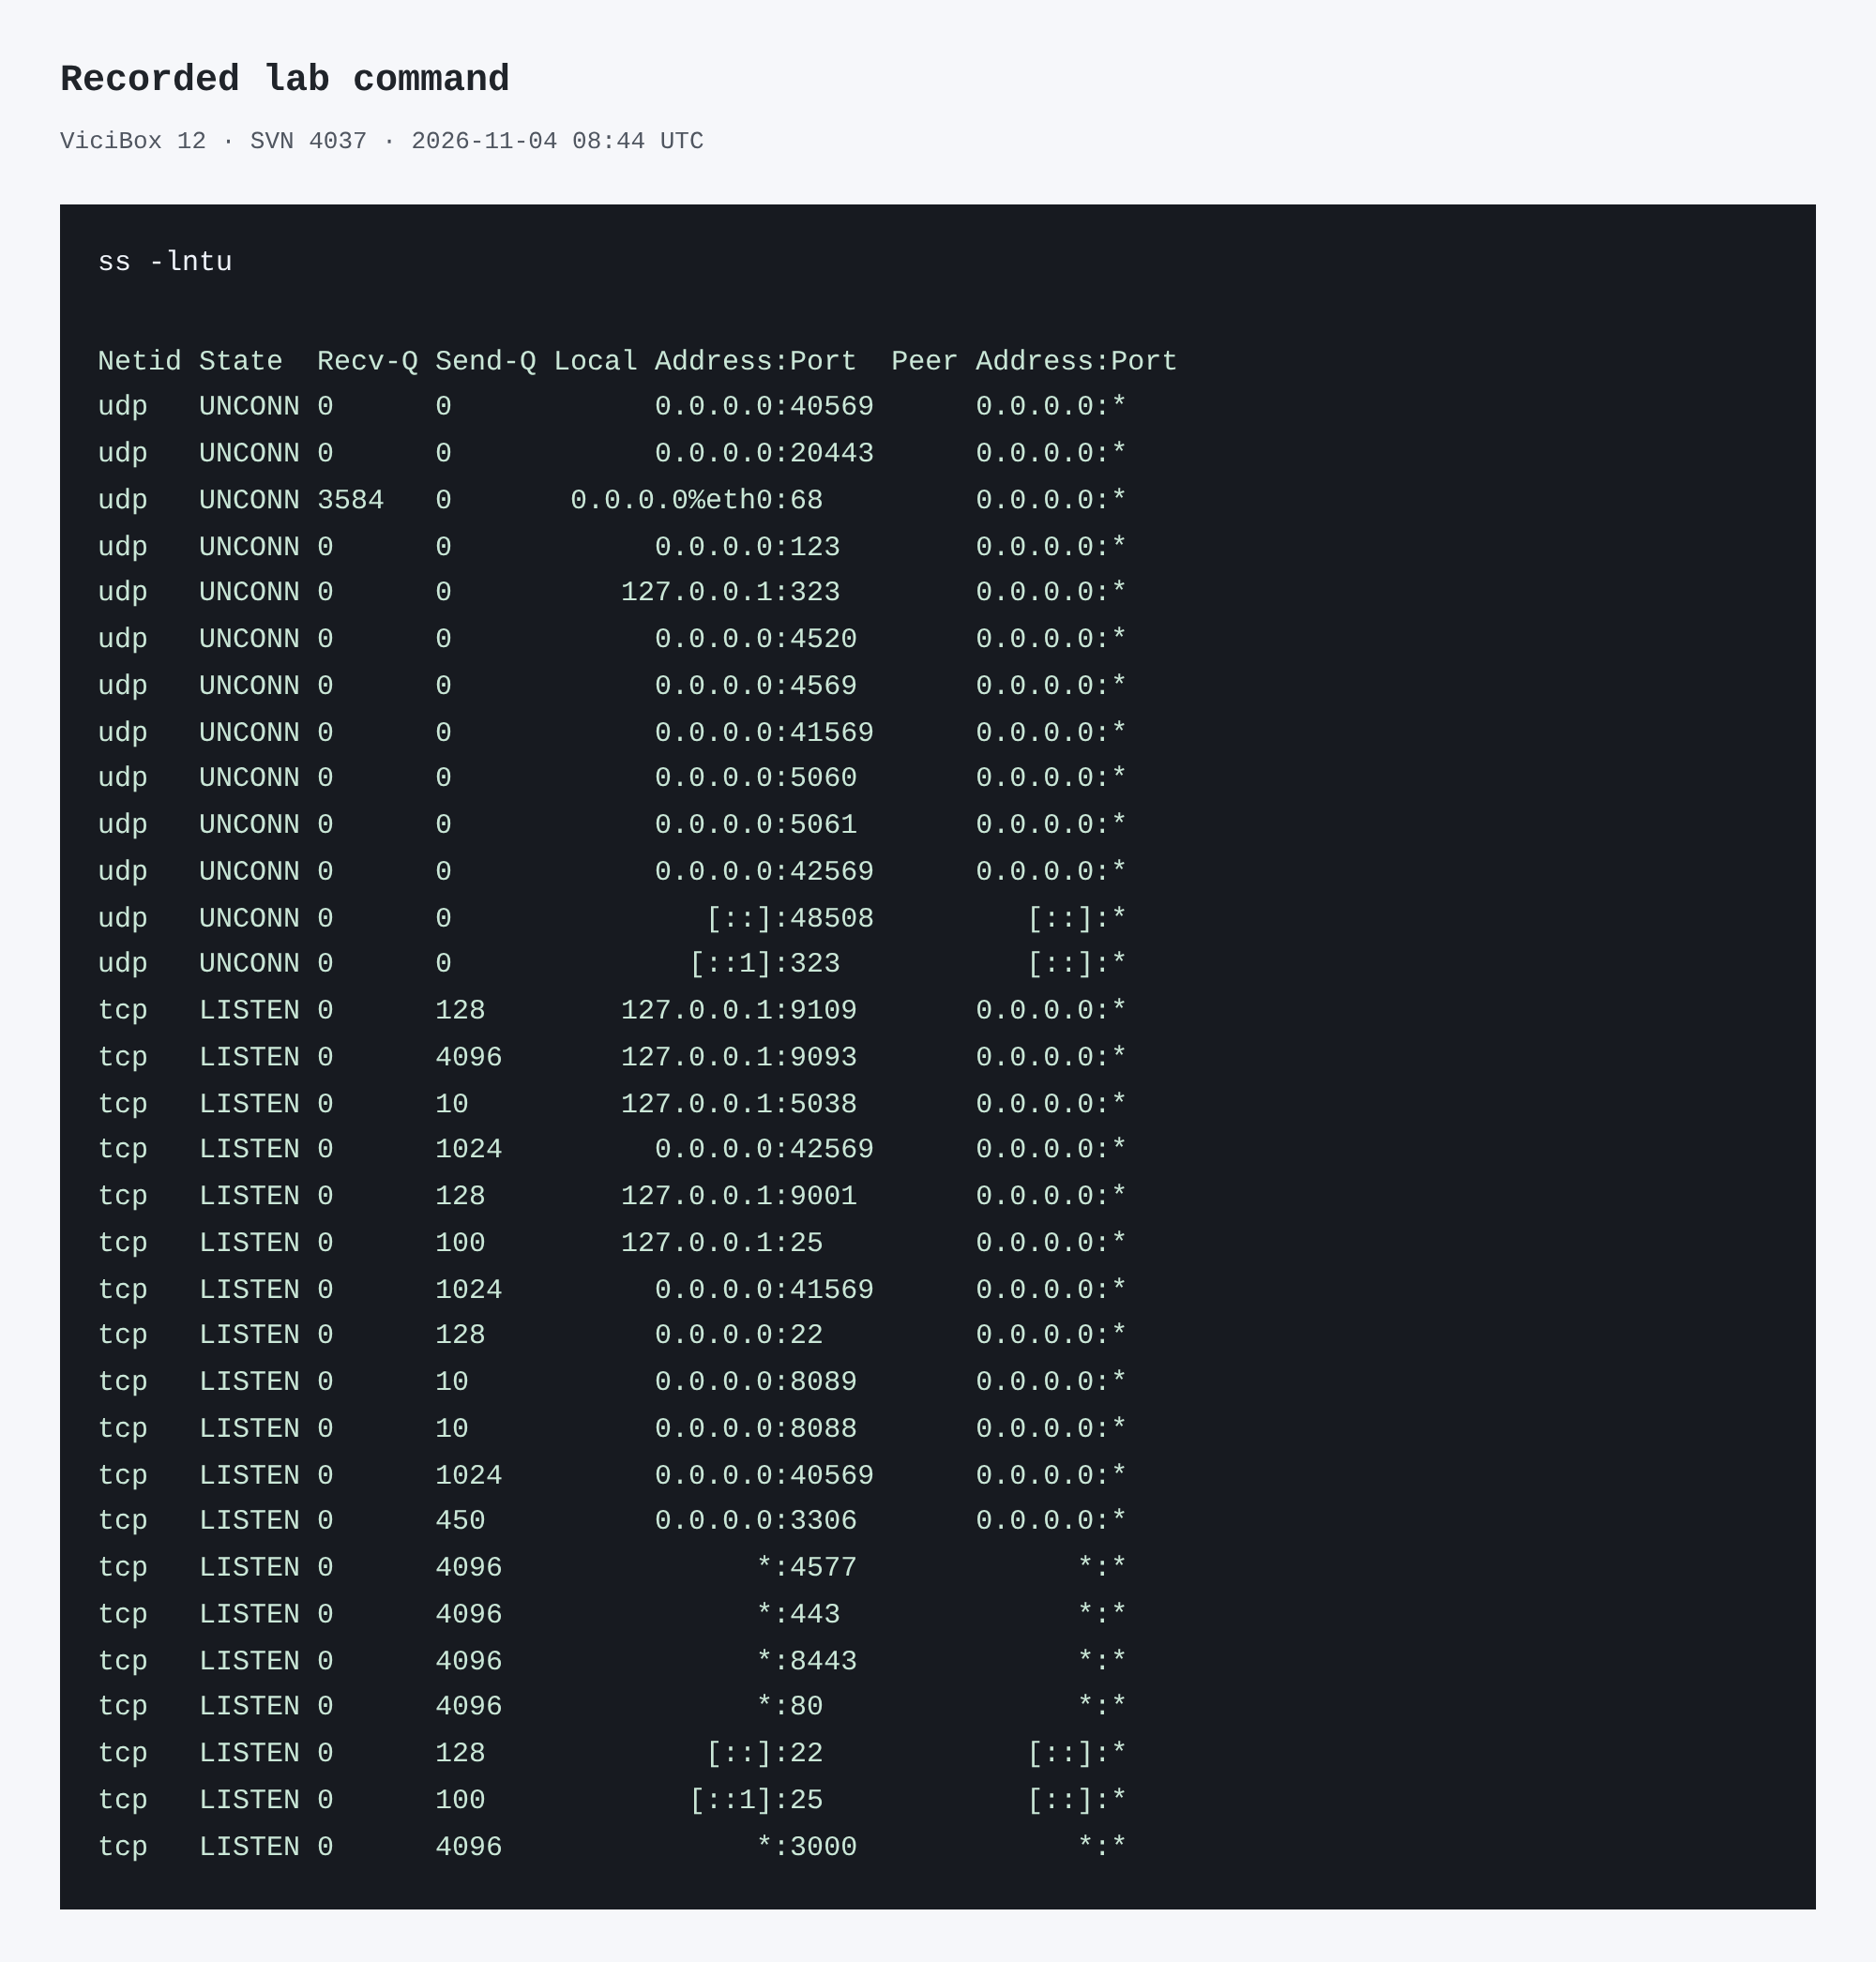
Capture details
Deployment-specific addresses masked. This inspection does not establish a completed call or restore.You should seeIf the expected listener is absent, investigate the service first. If it is present but the remote test fails, confirm that the client used the intended destination address and port, then inspect host and network access policies and service behavior with their owners. This check alone cannot locate the failure.
03 / 03
3. Narrow the failure
- Record client, destination name, resolved address, port, time and the exact error without credentials.
- Check the service status and then ask network owners to inspect routing and firewall policy along the authorized path.
- For HTTPS, verify the certificate separately; for SIP and RTP, test the relevant signaling and media paths separately.
You should seeDo not infer RTP audio from a successful web or TCP port check.
Checks and sources
What was checked
- The hostname lookup is a reader-run instruction and may contact the configured resolver; no lookup result is shown. The socket capture is a point-in-time view of the inspected host.
Primary references
Sources
- ip address manualLinux man-pages · accessed November 4, 2026
- ss manualLinux man-pages · accessed November 4, 2026